 Skip to content
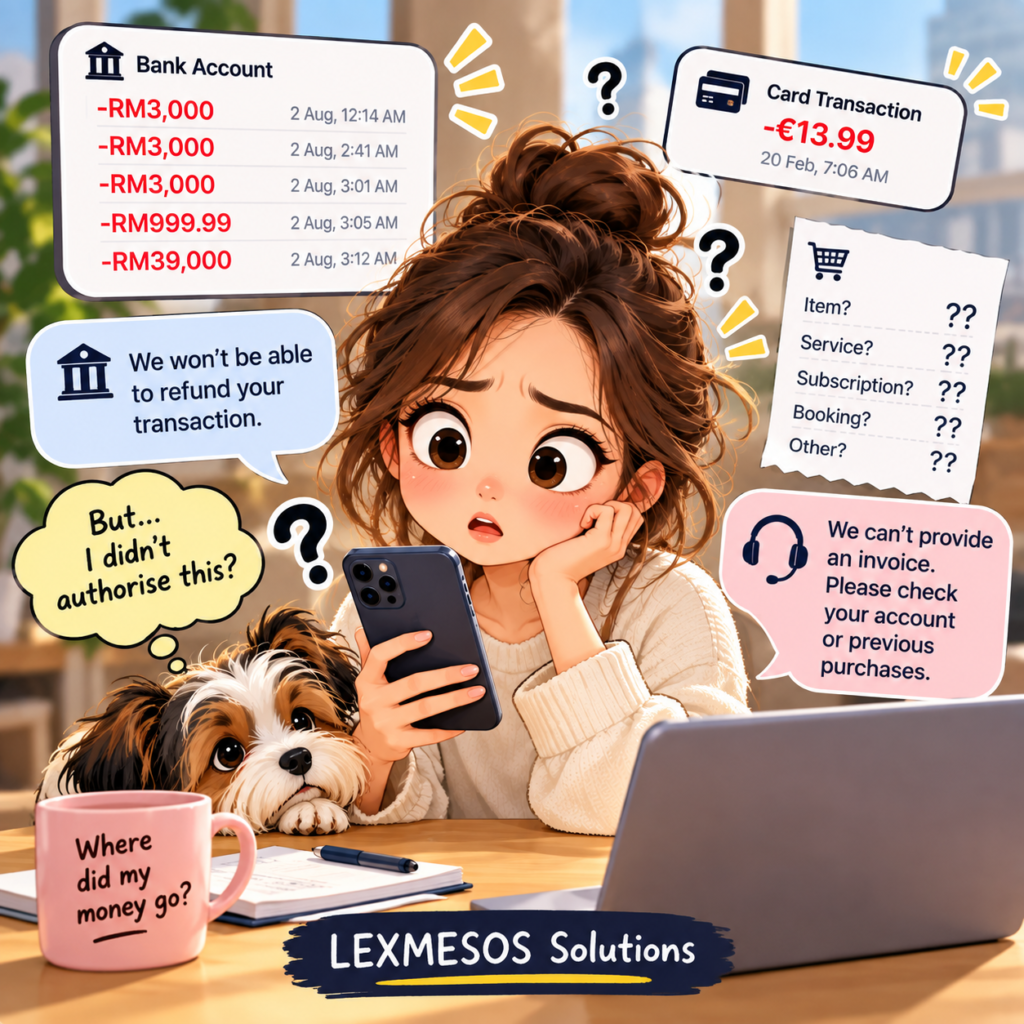
Imagine opening your banking app and seeing money gone.
You did not make the payment.
You did not approve it.
You report it to the bank.
Then comes the frustrating part: instead of someone explaining how the payment was authorised, you find yourself trying to prove that you did not do something.
That sounds simple when the amount is €13.99.
It becomes frightening when the amount is almost RM49,000.
And devastating when it is someone’s retirement savings.
A Malaysian retiree lost almost RM49,000
In September 2026, Malaysian media reported the case of a retiree identified as Mr Lo. (Utusan Sarawak)
According to reports, RM48,999.99 left his Maybank account through five transactions between 2 and 3 August 2026.
The transactions reportedly included RM3,000, another RM3,000, another RM3,000, RM999.99 and finally RM39,000 at 3:12 a.m.
Mr Lo maintained that he did not authorise the transactions. Maybank subsequently offered RM9,799.99, approximately 20% of the loss, as a full and final settlement. He rejected the offer.
That raises an obvious question.
Why 20%?
The publicly available reports do not provide Maybank’s detailed investigation findings explaining how that percentage was reached.
So it would be wrong to conclude from the offer alone that Maybank was responsible for 20%, or that Mr Lo was responsible for the other 80%.
But the case raises a much bigger issue.
When a customer says:
“I didn’t authorise these transactions.”
What happens next?
And who has to prove what actually happened?
It happened to me too. Mine was €13.99.
This story caught my attention because I experienced a much smaller version of the same problem.
On 20 February 2024, I noticed a €13.99 Ryanair transaction on my Revolut account.
I did not recognise it.
I did not have a Ryanair transaction on that date.
I treated it as an unauthorised transaction, reported the matter and replaced my card.
My dispute was subsequently declined.
So I contacted Ryanair.
My question was remarkably simple:
What was the €13.99 for?
I asked for the invoice or information identifying what had supposedly been purchased.
I could not obtain an explanation identifying the transaction.
Of course, €13.99 is nowhere close to RM48,999.99.
Most people are not going to spend months fighting over €13.99.
Neither did I.
But that’s exactly what makes the experience interesting.
Because whether the unexplained transaction is €13.99, RM49,000 or RM166,000, the underlying question doesn’t change:
Who has to prove that I authorised the payment?
Malaysia doesn’t automatically make the bank pay
There is an important misconception to clear up.
An unauthorised transaction does not automatically mean the Malaysian bank must refund 100% of the money.
It is based on shared accountability.
Customers have responsibilities. Banks have responsibilities.
For example, customers are expected to protect their credentials and avoid risky behaviour such as downloading harmful applications despite warnings.
But banks are also accountable where weaknesses in their security controls contribute to a loss. BNM specifically identifies failure to detect and prevent suspicious transactions outside a customer’s normal behaviour as something for which a bank may be accountable.
That is an important point.
The question should not simply be:
“Was the customer’s username, password or banking device used?”
It should also include:
Was this transaction normal for this customer?
Were there unusual transaction times or amounts?
Were fraud-detection systems triggered?
Were proper authentication measures used?
Did the customer receive transaction notifications?
How quickly did the customer report the transaction?
And ultimately:
What does the evidence actually show?
Then another Malaysian case reached court
Only a few months before Mr Lo’s case became public, the Kuala Lumpur Sessions Court dealt with a much larger unauthorised-banking dispute.
In Chan Yan Li’s case against Maybank, RM166,000 was transferred through a series of transactions in 2021. (New Straits Times)
Chan said she had never approved the transactions and had not received the relevant TAC messages.
Maybank disputed her case and relied on evidence including the use of the correct banking credentials and its records concerning TACs and notifications.
But the court examined more than whether the banking system had technically processed the transactions.
The transaction pattern mattered.
According to reporting on the judgment, the court found that the unusual activity should have raised suspicion and that the bank had failed adequately to monitor the accounts.
In May 2026, the Sessions Court found Maybank negligent and awarded Chan RM166,000.
That judgment does not mean Mr Lo will necessarily receive RM48,999.99.
They are different cases, involving different facts and evidence.
But put the two Malaysian cases beside each other and something important becomes clear:
How the transaction happened matters.
So does the bank’s monitoring.
And so does the evidence.
Now compare that with Europe
The European approach gives us another perspective.
Under the EU’s Payment Services Directive 2015/2366 (PSD2), where a customer denies having authorised a payment, the payment service provider bears the burden of proving that the transaction was authenticated, accurately recorded and not affected by a technical breakdown or other deficiency. (EUR-Lex)
But there is an even more important protection.
PSD2 expressly preserves the fundamental principle that merely showing that a payment instrument was used is not necessarily sufficient to prove that the customer authorised the transaction, acted fraudulently or failed, intentionally or through gross negligence, to protect their payment credentials.
That distinction matters.
A bank’s system might show:
The card was used.
The credentials were correct.
The payment was successfully processed.
But those facts do not necessarily answer the separate question:
Did the customer actually consent to this particular payment?
For an unauthorised payment, PSD2 also generally requires the payment service provider to refund the amount immediately and, in any event, no later than the end of the following business day after becoming aware of or being notified of the transaction. There are exceptions, including where the provider has reasonable grounds to suspect fraud by the customer and communicates those grounds to the relevant national authority.
This does not mean every European consumer who says “I didn’t authorise it” automatically gets to keep a refund regardless of the evidence.
It means that simply saying:
“Our system shows your card was used.”
is not necessarily the end of the investigation.
And there is a European court case that shows just how important the distinction between authentication and actual consent can become.
The EU Court of Justice: authentication is not the end of the story
The case concerned the predecessor EU Payment Services Directive rather than simply being another modern card-fraud dispute, so its facts are different from both my Ryanair transaction and the Malaysian cases.
But its treatment of consent, authentication and burden of proof is extremely relevant.
The Court described the EU liability regime as resting on three interconnected elements: notification by the user, the burden of proof on the payment provider and, where the necessary proof is absent, potential liability of the provider.
The Court emphasised that the burden-of-proof mechanism is designed in favour of the payment-service user: the provider must establish that the transaction was authenticated, accurately recorded and entered into the accounts.
That gets to the heart of the problem.
A computer system can show that a transaction happened.
That does not automatically answer:
Who authorised it?
Why should the consumer have to investigate the payment system?
Think about what information an ordinary customer actually possesses.
You can see:
RYANAIR – €13.99
or:
TRANSFER – RM39,000
That’s about it.
The consumer generally cannot see the bank’s fraud-detection data.
They cannot inspect authentication logs.
They cannot independently retrieve merchant payment records.
They cannot see what device initiated a transaction unless that information is provided.
They cannot inspect the acquiring bank’s records.
They may not know whether a payment was processed using stored credentials, strong customer authentication or another mechanism.
The banks, payment providers and merchants hold much of that information.
That information imbalance is precisely why the burden of proof matters so much.
Telling someone:
“Prove you didn’t authorise it.”
can be an extraordinarily difficult demand.
How exactly do you prove that you didn’t do something?
But this doesn’t mean every customer claiming fraud should automatically get their money back
That wouldn’t be sensible either.
A proper investigation may reveal that the customer approved the transaction.
Someone may have disclosed credentials.
There may be evidence of gross negligence.
A transaction may have been genuinely authorised but later disputed because the customer was unhappy with the product or service.
A recurring or merchant-initiated payment can also create a completely different factual situation.
These distinctions matter.
That is why the answer should not automatically be:
“The customer is right.”
But neither should it automatically be:
“The bank’s system processed it, therefore the customer authorised it.”
The evidence has to tell the story.
“Final decision” doesn’t necessarily mean the dispute is finished
There is another lesson Malaysian consumers should know.
If a bank issues a final decision and the customer remains dissatisfied, there may still be another avenue before going to court.
Generally, a consumer can refer the dispute to FMOS within six months of receiving the financial institution’s final decision. If the institution does not respond within 60 days of the original complaint, the consumer may also be able to proceed to FMOS.
There is an interesting additional protection in the FMOS rules.
Financial institutions are supposed to tell customers about FMOS and the six-month deadline in their final decision. Where the institution fails altogether to tell the customer about that deadline in its communications, the FMOS rules provide that the complaint is not subject to that filing deadline. (FMOS)
That is something worth knowing before throwing away a rejection letter.
A bank saying:
“This is our final decision.”
doesn’t necessarily mean:
“You have no other options.”
€13.99 taught me something
I did not pursue my €13.99 dispute through years of proceedings.
Realistically, very few consumers would.
But looking back at it beside these Malaysian cases, I think the amount almost distracts from the real issue.
Imagine if it hadn’t been €13.99.
Imagine €1,399.
Or €13,999.
Or your retirement savings.
Suddenly the question that seemed too small to fight about becomes extremely important.
When money leaves someone’s bank account without their claimed permission, there needs to be a proper investigation.
Consumers should be expected to cooperate and protect their accounts.
Banks should be allowed to rely on genuine evidence showing authorisation, fraud or customer fault.
But where the customer denies authorising a payment, there should also be a clear and understandable answer to a remarkably simple question:
What evidence shows that I said yes?
Because “the payment went through” and “you authorised the payment” are not necessarily the same thing.
And whether the missing amount is €13.99 or someone’s lifetime savings, that distinction matters.
If You Notice an Unauthorised Transaction
If you notice a transaction you do not recognise, contact your bank or payment provider immediately. Do not wait for the merchant to respond before notifying the bank.
Freeze or block the affected card if necessary, secure your banking credentials, and keep screenshots of the transaction and all communications. Make it clear that you are reporting an unauthorised transaction, rather than simply requesting a merchant refund.
If the bank rejects your claim, ask for the reason in writing and the evidence showing how the transaction was authorised. You should also check whether the decision can be escalated to the relevant financial ombudsman or regulator.
Most importantly, act quickly. Unauthorised transaction claims and external complaint procedures may be subject to strict notification and filing deadlines.
Keywords: The key topics are unauthorised bank transactions, bank fraud Malaysia, Maybank unauthorised transactions, PSD2 unauthorised payments, EU banking law, bank liability, payment fraud, consumer banking protection, Revolut disputes, Ryanair unauthorised charges, Financial Markets Ombudsman Service, online banking fraud, burden of proof and payment authorisation
24 September 2026